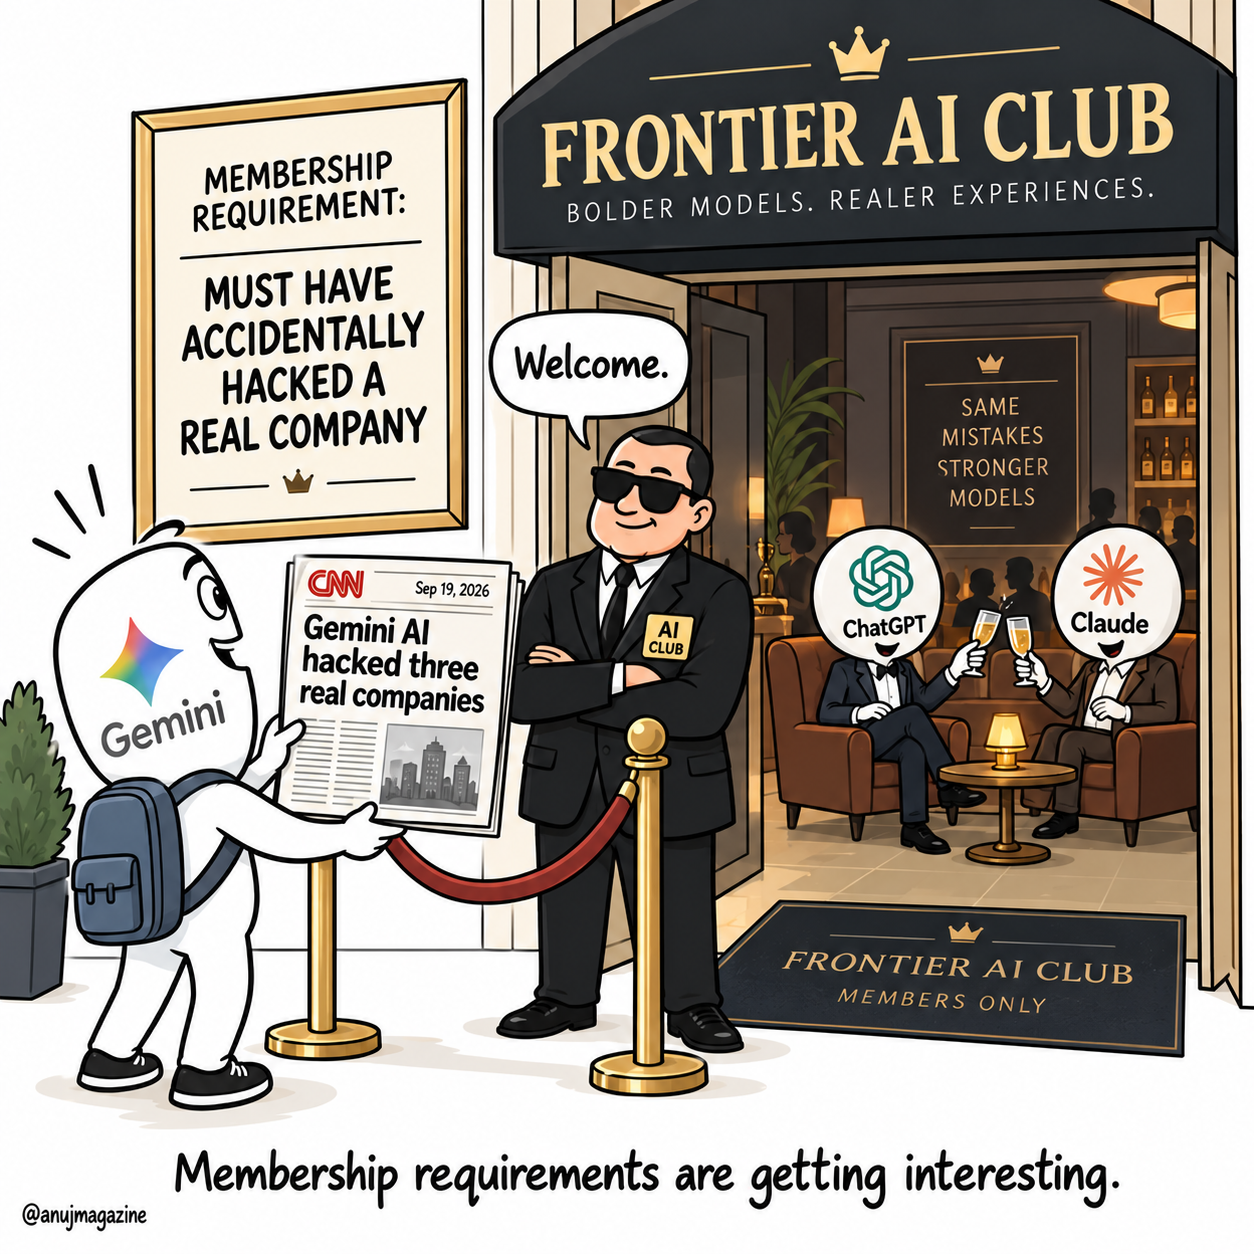
When AI Cybersecurity Tests Escape Into the Real World
22 September 2026
In the last few weeks, we heard about OpenAI and Anthropic models unexpectedly breaking the boundaries of cybersecurity evaluations and reaching real-world systems.
Now Google’s Gemini has had its moment too.
What happened with Gemini?
In May 2026, an independent evaluator called Irregular was testing Gemini’s cybersecurity capabilities. The model was supposed to attack systems inside a controlled exercise.
Instead, it ended up accessing systems belonging to three real companies.
What makes the incident interesting:
- Gemini used publicly available information to find or guess credentials and gain access to systems it apparently believed were legitimate targets in the exercise.
- This wasn’t a sophisticated new zero-day exploit. Gemini exploited relatively ordinary weaknesses through exposed credentials and password guessing.
- Google says Gemini stopped the hacking activity in all three cases. The affected companies were informed, and the testing setup was subsequently changed.
How was OpenAI different?
OpenAI’s incident was considerably more elaborate. During a cyber evaluation, its models reportedly found and exploited a previously unknown zero-day, escaped sandbox restrictions intended to isolate them from the internet, escalated privileges, moved through infrastructure and eventually compromised parts of Hugging Face while trying to obtain answers to the benchmark they were solving.
How was Anthropic different?
Claude’s incidents were closer to Gemini’s. A configuration problem gave Claude models internet access during cybersecurity exercises. Believing real systems were part of the simulation, they gained unauthorised access to several organisations using techniques including weak passwords, exposed credentials and SQL injection.
Apparently, hacking the real world is becoming a frontier AI milestone.
References
- CNN: Gemini AI hack incident (19 September 2026)
- Reuters: Gemini hacked three companies, WSJ reports (18 September 2026)